// MEDIA AND PRESS · HANS STUDY

Media and press. Hans Study. Independent. On the record.

Hans Study is available for press interviews, podcast guesting, expert commentary, background briefings, and conference panels. Everything a producer or a reporter usually has to ask for is on this page: bios, topics, headshots, quotes, research, and the ground rules.

At a glance

Name
Hans Study, CISSP
Role
Independent network and security consultant
Based
Ontario, Canada. Eastern time.
Works across
Canada and the United States
Formats
Remote video or audio, in person in Ontario, written Q&A, background briefings
Setup
Own studio: 1080p video, 48 kHz audio, wired connection
Languages
English
Hosts
StudyByt3s podcast

Topics Hans speaks to

CPCSC and CMMC

Canadian defence suppliers in US and Canadian supply chains now face mandatory cybersecurity certification. CMMC Phase 1 enforcement began November 2025; Phase 2 was suspended July 13, 2026, pending review. CPCSC Level 1 has been in select contracts since summer 2026, with Level 2 planned for April 2027 to March 2028 in PSPC's timeline. Hans speaks to the technical realities of meeting NIST SP 800-171 controls in environments designed before the rules were written, and wrote the free CPCSC readiness guide.

The cyber hygiene of small business

The State of Cyber Hygiene series looks at thousands of small-business domains, region by region, using public DNS and web signals only. How many can be impersonated by email, how many run a web stack with a known remote-code-execution flaw, and why the fixes are cheap and still not done. Hans can speak to method, limits, and any region in the series. No business is ever named.

OT and ICS network security

Critical infrastructure runs control systems where a network failure or a breach has consequences beyond data loss. Hans has worked on OT segmentation, IT and OT convergence, and NERC CIP advisory across Canadian utilities and US critical infrastructure operators.

IT and physical security convergence

The network is the security system now. Cameras, access control panels, and intrusion devices all run on IP. The people responsible for the network and the people responsible for the physical security system rarely talk to each other. That gap is where most security incidents now start.

Email domain security

SPF, DKIM, and DMARC, explained for a general audience and for installers. Why a domain with no enforcement can be impersonated by anyone, what it costs a small business when it happens, and why the fix is a DNS record rather than a product.

Wireless network design and survey

Predictive design, validation survey, and troubleshooting on enterprise Wi-Fi. Trained on Ekahau and CWNP material. Field experience across Cisco, Aruba, and Meraki wireless in airports, transit, government, and enterprise environments. Why most enterprise Wi-Fi under-performs, and where the gap between the marketing material and the operational reality shows up.

Genetec, C-CURE, Milestone, Avigilon, Axis, Axon

Platform expertise across the major physical security platforms. Architecture mistakes, common deployment failures, sizing, federation at scale, release reviews, and the gap between integrator marketing and field reality.

Mobile and computer forensics

Trained in mobile device forensics and computer forensics. Field experience with evidence networks and isolated investigative environments for law enforcement and corporate investigations. Chain of custody, evidence network design, and the infrastructure side of digital forensics that the tools-and-techniques content skips.

Independence and conflict of interest

The conflict-of-interest problem in a market where almost every consultant carries vendor partnerships and earns margin on what gets installed. Why independent assessment exists, what it costs to run that way, and who actually pays for it.

Teaching technical material

Hans taught Cisco CCNA, introductory and advanced networking, information security, and Microsoft Windows Server and Workstation at the post-secondary level for multiple years. Hundreds of students went through those programs. The teaching shaped the advisory work. Both depend on being able to explain why, not just how.

For podcast and show producers

Hans hosts StudyByt3s and guests on other shows. What a producer gets:

  • A guest who opens on a specific system, version, or failure, not a vendor pitch and not a list of best practices.
  • Comfortable live or recorded, video or audio only, solo or on a panel.
  • Own studio, so the audio and video arrive clean on your side.
  • No clients named, no products pushed, no speculation about an incident beyond what is public.
  • Practitioner questions from your audience are welcome, including the awkward ones.

To make a booking easy, send the show name, the audience, the format, the date and time with time zone, and 2 or 3 questions you want to open with. Episode angles that work well:

  • Why the camera network is the weakest part of the building security system
  • A Canadian defence supplier's first CPCSC audit: what the assessor actually opens
  • The small-business email flaw that costs nothing to fix and almost nobody fixes
  • What a security system looks like after installation versus what was designed
  • Uptime is not availability: the number that gets misused in every RFP
  • Independent review in an industry that earns its living on margin

Bios

Three lengths, ready to paste. Attribute as Hans Study, CISSP, independent network and security consultant, hans.study.

Short

Hans Study, CISSP, is an independent network and security consultant in Ontario, Canada. He works with public sector, defence, critical infrastructure, and enterprise organizations across Canada and the United States on compliance readiness, OT and IT network security, and the physical security systems that run on them. He hosts the StudyByt3s podcast and writes at hans.study.

About 60 words
Medium

Hans Study, CISSP, is an independent network and security consultant in Ontario, Canada, with more than 15 years in the field. He works with public sector, defence, critical infrastructure, and enterprise organizations across Canada and the United States on compliance readiness, OT and IT network security, and the physical security systems that run on them. He built and sold an earlier security practice, and the current one sells no products, carries no margin, and takes no commissions. He is the author of 3 Study Guide titles for integrators and defence suppliers, taught networking and information security at the post-secondary level, hosts the StudyByt3s podcast, and publishes the State of Cyber Hygiene research series at hans.study.

About 120 words
Long

Hans Study, CISSP, is an independent network and security consultant based in Ontario, Canada. He works with public sector, defence, public safety, critical infrastructure, and enterprise organizations across Canada and the United States. His focus is compliance readiness under CPCSC and CMMC, OT and IT network security, and hardening the Windows, Cisco, and Aruba infrastructure that physical security and critical systems run on, with Genetec Security Center as the reference platform for the VMS work.

He started the way many people in the field do, installing small-business networks and CCTV systems, grew that into his own IT firm, and built and sold an earlier security practice. The current practice is deliberately independent: no products, no margin, no commissions, and no installation work. Only advice is sold. He is the author of 3 Study Guide titles, including the free Study Guide to CPCSC Readiness for Canadian defence suppliers, and taught Cisco CCNA, networking, information security, and Windows Server at the post-secondary level for multiple years.

He publishes the State of Cyber Hygiene series, an outside look at the email and web security of thousands of small-business domains, region by region, using public signals only. He hosts the StudyByt3s podcast, reviews security and network products on the same independent terms as the consulting, and has been quoted in CIO on the EU Cyber Resilience Act.
About 260 words

Research available for stories

The State of Cyber Hygiene series is an outside look at the email and web security of small-business domains, built from public DNS and web signals only. Nothing is scanned, probed, or logged into. Each report explains its method and its limits, and regional cuts are published for several Ontario regions with more to come.

Reporters can ask for a walkthrough of the method, comment on a specific finding, a regional comparison, or a plain-language explanation of what a reader can check on their own domain. Two things are fixed: no business is ever named, and exposure figures are always a floor, never a count of what is actually vulnerable.

Published work

Author of the Study Guide series, field references for integrators and defence suppliers, 3 titles published in 2026:

Articles, hardening guides, and release reviews are published at hans.study/articles/ and syndicated to DEV Community. Free tools, including the open-source PortProof, are at hans.study/tools/. Review copies and bulk orders of the books: book@hans.study.

Press appearances

If you have published a piece that quotes or references Hans Study, send a note to media@hans.study and it gets linked here.

Headshots and artwork

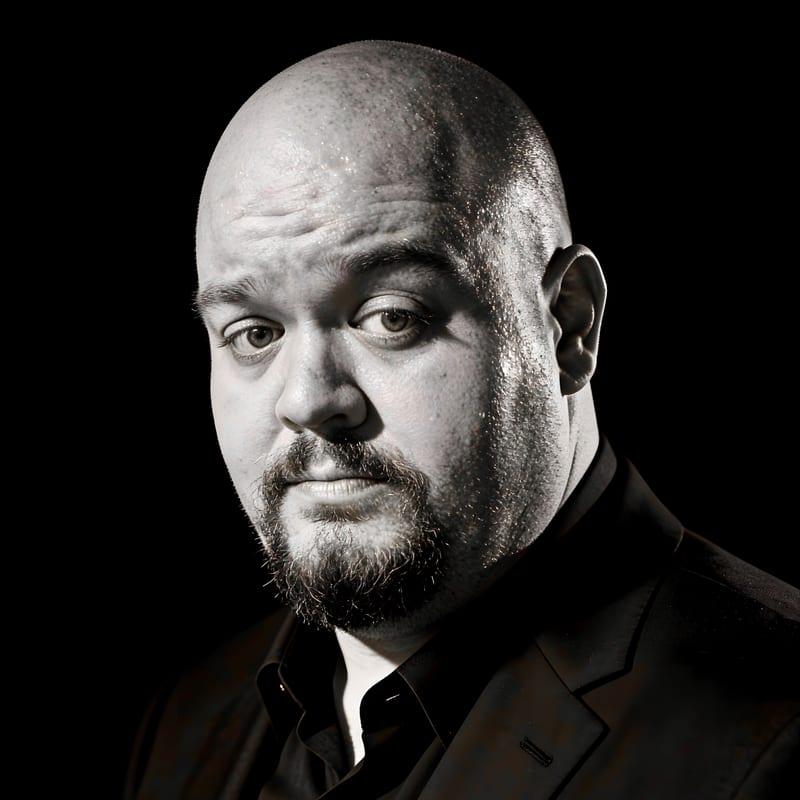
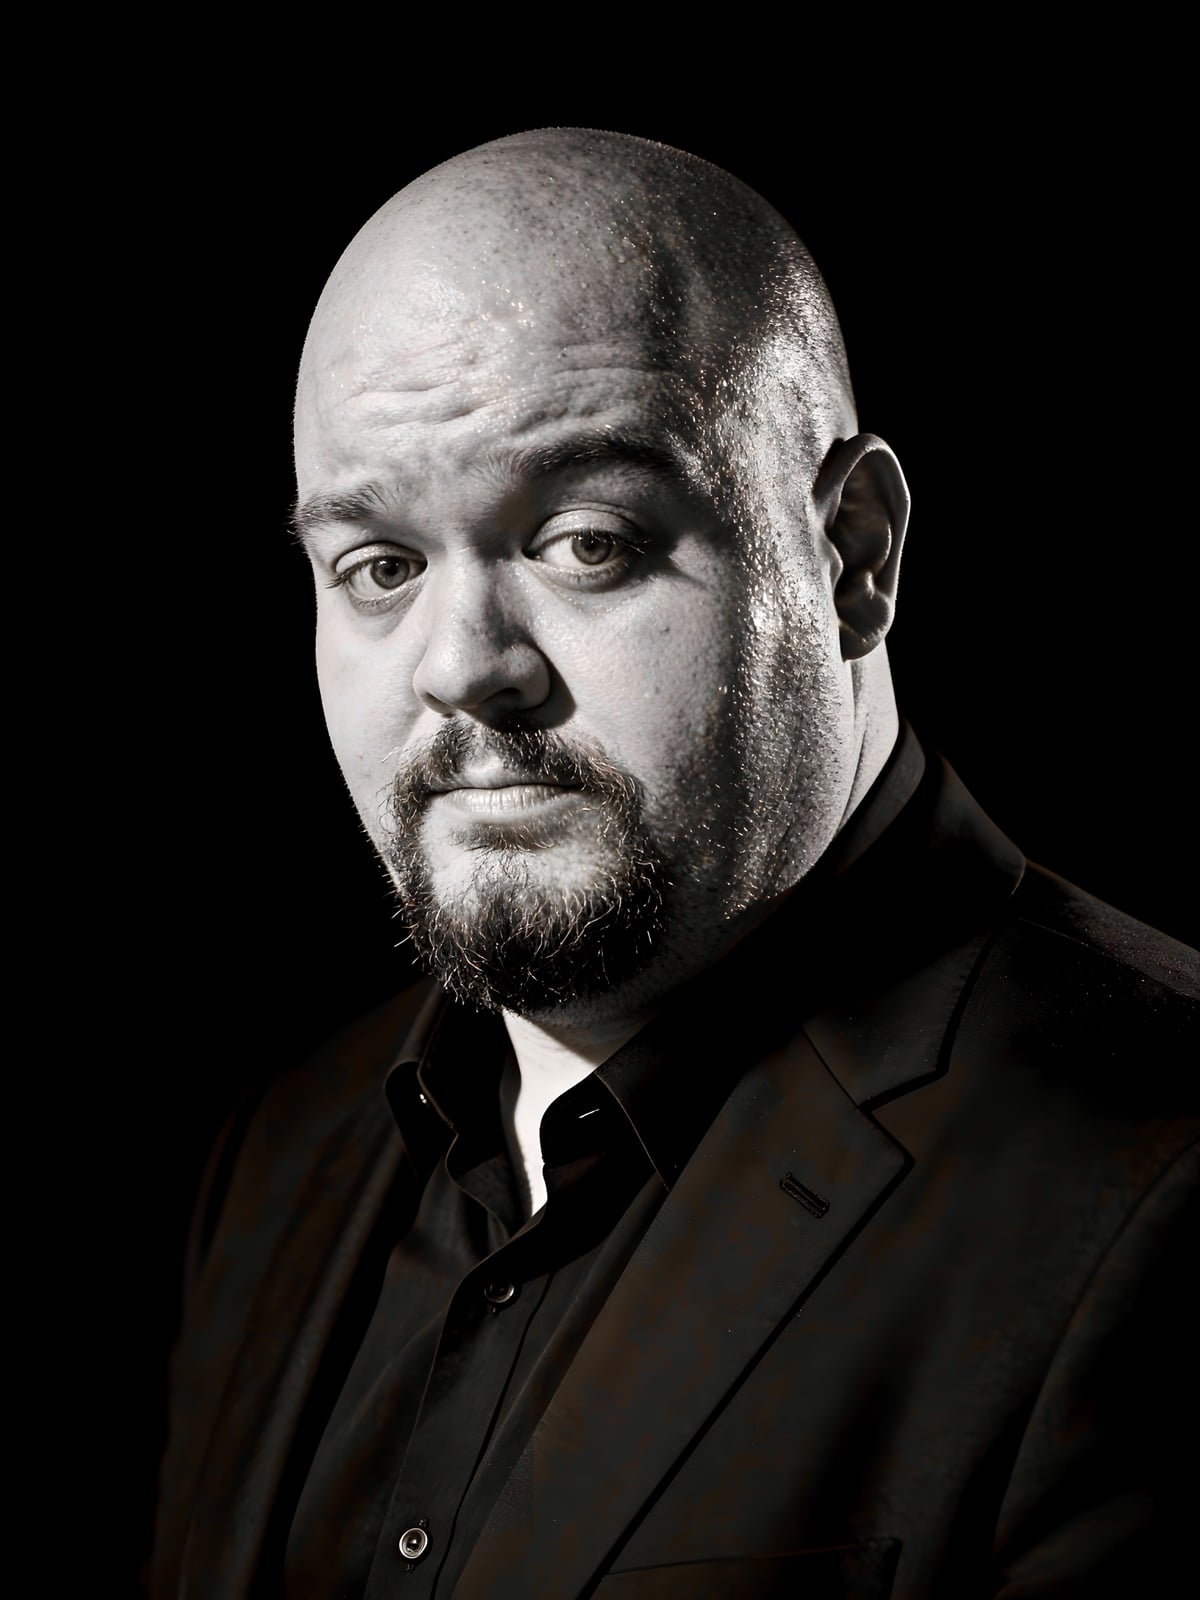
Approved crops for editorial use with coverage. Download the file as supplied; it carries the credit, copyright, and licence in its metadata.

Credit line: Photo: Hans Study / hans.study

Usage: editorial use with the credit line. Keep the approved crop, and don't recolour the image or add effects. Anything beyond editorial use needs written permission from media@hans.study.

Quote sheet

Ready-to-use pull quotes for stories on security posture, defence in depth, and the work that does not require AI. Attribute to Hans Study, CISSP, independent network and security consultant (hans.study). No clearance required for these specific quotes.

The low hanging fruit is still sitting there in plain view: default credentials, exposed management interfaces, ancient firmware, shadow devices nobody bothered to inventory, and access control lists written in a rush, never reviewed, and left to rot for years. None of that needs AI to find it. It needs someone to stop ignoring obvious problems because they are boring or they take time.

On the basics, and why AI is not the gap.

Security is not about making targets impenetrable or untouchable. It is about making them not worth the effort. I have always described security and security controls as a series of speed bumps. They are there to slow an attacker down, make the path annoying, and make the whole thing feel like more trouble than it is worth. Some of those speed bumps are bigger than others. Smaller cars will not make it over all of them, and that is a successful day. Someone with enough determination, or a big enough vehicle, may still get where they are trying to go. The ride should be miserable for them. That is good defense.

On defence in depth.

Need a quote tailored to your angle? Email media@hans.study with the topic and deadline.

Ground rules

  • On the record by default. Background or off the record is fine when agreed before the conversation starts, not after.
  • Clients and their sites are never named or described in a way that identifies them. That holds for former clients too.
  • No comment on an active incident beyond what the affected organization has made public, and no guessing at attribution.
  • No product endorsements in press. Where a product comes up, the review terms apply and the review is the record.
  • Corrections are welcome. If something attributed to Hans is wrong, email media@hans.study and it gets fixed at the source.

For journalists on deadline

Stories on a deadline

If you are working a story on tight deadline and need a quote on infrastructure security, OT, physical security, small-business cyber hygiene, or compliance, email media@hans.study with "deadline" in the subject and the date you need it by, so it gets read first.

Brand assets and usage

Marks, palette, typography, and the full design system are published at hans.study/brand/. The page includes individual asset downloads, a bundled ZIP, the colour palette, typography references, every callout and component used across the site, and the licence and usage terms. Use beyond the permitted editorial scope listed there requires written permission to media@hans.study.

Quote permissions

Direct quotes from articles published on hans.study are permitted with attribution to "Hans Study (hans.study)" and a link back to the source article. Reprint of full articles requires written permission. Email media@hans.study.